
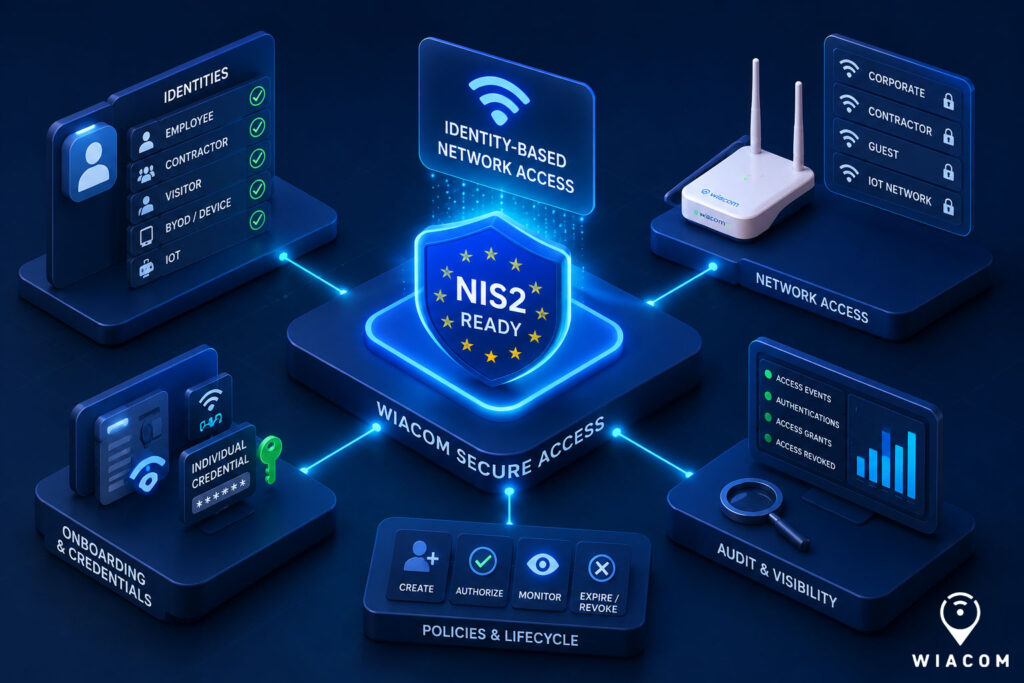
NIS2 network access control means being able to show who is authorised to connect to your network, how that access was granted, and when it was changed or removed. For organisations running Cisco, Aruba, UniFi and other WiFi platforms across multiple sites, Wiacom provides a common identity and access layer, with individual credentials issued through Guest Connect, RADIUS authentication, Passpoint and credential lifecycle controls, without replacing the existing infrastructure.
NIS2 puts stronger emphasis on access control, authentication, accountability and operational security.
For organisations operating multiple sites, the challenge is often not defining the policy. It is applying it consistently across the network, especially when the infrastructure is mixed.
Cisco at headquarters. Aruba in warehouses. UniFi at smaller branches. Different controllers, different authentication methods and different troubleshooting tools.
Wiacom can provide a common identity and network-access layer above that infrastructure.
Why NIS2 matters for WiFi access
The NIS2 Directive sets EU cybersecurity risk-management requirements for essential and important entities across sectors such as healthcare, energy, transport, manufacturing, digital infrastructure and ICT service management. Its measures include access control, authentication and incident handling.
Wireless networks are a common place where these controls become inconsistent, especially across multiple sites and vendors. Wiacom supports healthcare and enterprise and business WiFi environments where individual, auditable access matters.
One access layer across Cisco, Aruba, UniFi and mixed WiFi vendors
Wiacom is vendor agnostic.
Organisations and managed service providers can use a common approach to onboarding, identity and network access while continuing to operate the wireless infrastructure already deployed.
Depending on the environment, Wiacom can support access through:
- individual iPSK / MPSK / PPSK credentials;
- Passpoint profiles;
- RADIUS-based authentication, including WPA2/WPA3 Enterprise;
- identity-based onboarding through Guest Connect, including offsite onboarding;
- temporary or expiring credentials;
- captive portal access where required.
Guest Connect is the onboarding entry point for this. Staff, contractors and suppliers can register or be invited, including offsite before they arrive, and receive either a unique PSK or a Passpoint profile for their own devices, depending on what the network supports.
The objective is simple:
Identity → individual access → controlled lifecycle → audit visibility
without requiring every location to use the same WiFi vendor.
Replace shared WiFi passwords with individual credentials (iPSK, MPSK, PPSK)
Shared WiFi passwords make individual access difficult to control, even with a rotation mechanism in place.
Wiacom can associate access with a specific user, contractor or device instead.
An individual credential can be created, restricted, expired or revoked without changing access for everyone else.
This is particularly useful for:
- employees
- contractors
- suppliers
- BYOD
- temporary personnel
- operational devices
- IoT
Because onboarding does not depend on being on site, staff and contractors can receive their individual access before they visit a location, without anyone sharing a common WiFi password.
For third-party access, the lifecycle can be straightforward:
Contractor invited through Guest Connect → unique PSK or Passpoint profile issued → authorised network access → credential expires → access revoked
ENISA’s technical implementation guidance for NIS2, which is non-binding, specifically addresses access control, authentication, logging and evidence around authorised access.
NIS2 and managed WiFi services for MSPs
NIS2 is also directly relevant to managed service providers and managed security service providers covered by the EU implementing requirements.
For an MSP managing many customers, standardising every customer’s network infrastructure is rarely realistic.
Wiacom provides another option:
- Customer A → Cisco Meraki
- Customer B → Aruba
- Customer C → UniFi
- Customer D → mixed environment
The underlying WiFi can remain different while Wiacom provides a common layer for identity, onboarding, access policies and operational visibility.
This allows an MSP to build a more consistent managed-access service without becoming dependent on a single wireless vendor. Wiacom also provides managed WiFi services and technical operations alongside MSP and customer IT teams.
WiFi authentication and RADIUS troubleshooting across vendors
Security and support increasingly overlap.
Wiacom can bring together the user journey and network authentication events to provide deeper troubleshooting visibility.
Identity → onboarding → credential → device → authentication → access decision → network
Support teams can investigate:
- failed authentication;
- expired credentials;
- incorrect access assignments;
- device-specific problems;
- repeated connection failures;
- onboarding issues;
- access attempts after expiry;
- inconsistencies between sites.
For MSPs, this provides advanced troubleshooting above the underlying WiFi vendor rather than requiring a separate operational process for every platform.
From one site to geographically distributed networks
NIS2-related network controls become harder to maintain as organisations expand.
A customer may operate:
- 10 branches in one country;
- 100 locations across Europe;
- multiple subsidiaries;
- different MSPs;
- different WiFi generations and vendors.
Wiacom is designed as a centrally managed SaaS layer, allowing identity and access workflows to be applied across geographically distributed environments.
Policies and onboarding processes can therefore remain consistent even when the infrastructure below them is not.
One organisation. Multiple countries. Multiple WiFi vendors. One access layer.
Credential lifecycle: create, authorise, expire, revoke
Network access should not remain active simply because a password is still known.
With Wiacom, access can follow a defined lifecycle:
Create → Authorise → Connect → Monitor → Expire or Revoke
The same model can be applied to users, contractors and devices.
This also creates clearer operational evidence when organisations need to understand who was authorised to access a network and when that access changed.
Operational visibility supports better evidence
ENISA’s implementation guidance includes logging, access records, authentication activity and audit trails among the mechanisms organisations can use to support cybersecurity controls and investigations.
Wiacom can help expose the network-access context behind those events:
- who connected;
- which device was used;
- where the connection occurred;
- how the identity was onboarded;
- which access method was issued;
- whether authentication succeeded;
- when the credential expired or was revoked.
This information can also be integrated into broader operational or security workflows.
Wiacom can also integrate with external SIEM, SOC and security automation platforms through APIs or custom integrations, allowing network-access events to become part of the organisation’s wider detection and response workflows.
Where required, Wiacom can also provide its own response and automation layer.
Authentication failures, expired credentials, unusual access patterns, repeated connection attempts or policy violations can be evaluated by Wiacom and used to trigger automated actions, alerts or remediation workflows.
This creates a broader operational model:
Access event → detect → correlate → respond → automate
For MSPs and distributed organisations, Wiacom can therefore operate either as a source of network-access intelligence for an existing SIEM/SOC stack, or as an active automation layer for access-related response.
For telcos and ISPs: Wiacom on existing CPE
Where supported, Wiacom can also be integrated with ISP-provided CPE using custom firmware or embedded software components, allowing service providers to extend Wiacom onboarding, identity, access control and operational visibility directly into the equipment already deployed at customer locations.
This creates another path for telcos and ISPs:
existing CPE → Wiacom-enabled firmware → identity-based access → central management and troubleshooting
without requiring the customer to replace the installed access equipment.
Implementation and support from Wiacom
Wiacom is not only a software licence. We can configure SSIDs, VLANs and access policies on your controllers, integrate RADIUS and WPA2/WPA3 Enterprise, deploy Passpoint and individual-credential access, connect your existing identity and business systems through APIs, and troubleshoot authentication issues across mixed-vendor environments.
We work alongside your IT team or MSP, with 24×7×365 support options for partners and enterprise customers. See Wiacom technical support and professional services.
How Wiacom fits into a NIS2 programme
Wiacom does not replace the broader NIS2 compliance programme.
It addresses a specific operational area:
identity-based network access, credential lifecycle, third-party access, authentication visibility and troubleshooting across distributed WiFi environments.
| Operational need | How Wiacom supports it |
|---|---|
| Individual access for staff, contractors and suppliers | Unique PSK (iPSK / MPSK / PPSK) or Passpoint profile per user, issued through Guest Connect |
| Offsite onboarding of staff and contractors | Remote registration or invitation through Guest Connect, before arrival on site |
| Third-party access that expires | Time-limited credentials with revocation |
| Authentication across mixed vendors | RADIUS and WPA2/WPA3 Enterprise across supported platforms |
| Evidence of who connected and when | Authentication and access-lifecycle records |
| Consistent onboarding across sites | Central SaaS layer, with EU hosting available |
| Faster troubleshooting | User-level view of onboarding, credential and authentication events |
For organisations and MSPs operating mixed wireless infrastructure, that can be particularly useful.
The network underneath may remain Cisco, Aruba, UniFi or another supported platform.
The access layer above it can become consistent.
Vendor agnostic.
Identity based.
Individually revocable.
Auditable.
Geographically scalable.
Built for MSP operations.
That is where Wiacom can support a stronger NIS2 network-access strategy.
NIS2 network access: frequently asked questions
What is NIS2 network access control?
It is the ability to show who is authorised to connect to a network, how that access was granted and when it was changed or revoked, as part of NIS2 risk-management measures.
Does Wiacom make an organisation NIS2 compliant?
No. Wiacom supports identity-based network access, credential lifecycle and authentication visibility, which are one part of a wider NIS2 compliance programme.
Can NIS2 access controls be applied across Cisco, Aruba and UniFi WiFi?
Yes. Wiacom operates above compatible WiFi infrastructure, so one identity and access model can apply across different vendors without replacing the existing network.
How can contractor WiFi access be controlled?
By issuing an individual, time-limited credential that can be restricted, expired or revoked without affecting other users. With Guest Connect, contractors and staff can onboard remotely and receive a unique PSK or Passpoint profile before they arrive on site.
What is Wiacom Guest Connect?
Guest Connect is Wiacom’s onboarding workflow for issuing individual WiFi access. It can provide a unique PSK or a Passpoint profile and is used for guests as well as staff and contractors, including offsite onboarding before arrival.
Can MSPs use Wiacom across different customer networks?
Yes. Each customer can keep a different WiFi vendor while the MSP uses a common layer for identity, onboarding, access policies and operational visibility.
Where is Wiacom hosted and is it certified?
Wiacom is ISO/IEC 27001 certified and operated in the EU. Hosting is available globally, including EU-hosted environments for customers with NIS2-related data residency requirements.
One access layer. Mixed vendors. Multiple locations. Central control.
Wiacom is ISO/IEC 27001 certified, designed and operated in the EU, with hosting available globally, including EU-hosted environments for customers with NIS2-related data residency and compliance requirements, and customer-network deployments where required. For MSPs, telcos and distributed organisations, this adds another layer of assurance when Wiacom becomes part of the network identity, access and operational stack.
See more about Wiacom Access Features→ · Managed WiFi Services → · Request a demo →


