

Enterprise & Business WiFi: Identity, Authentication & Access Management
One WiFi Identity and Access Layer Across Your Business
Wiacom helps organisations manage how employees, contractors, guests and connected devices register, authenticate and access enterprise WiFi across offices, branches and distributed business locations.
Connect existing identity providers such as Microsoft Entra ID, Google Workspace, Okta, Auth0 and Ping Identity with WiFi onboarding. Provide individual credentials through WiFi Pass, secure profile provisioning through Passpoint Connect, and flexible Captive Portal, Guest Connect and Staff Connect workflows.
Wiacom operates as a software and services layer above compatible existing infrastructure, supporting multi-location and mixed-vendor WiFi environments without unnecessary network replacement.
Support Captive Portal, Staff and Guest Connect, individual WiFi credentials, Passpoint, RADIUS and policy-based access while connecting identity and network activity with wider operational, security and compliance workflows.
Enterprise WiFi Onboarding for Employees, Contractors, Guests and Devices
Modern business networks must support different users, devices and authentication requirements across the same WiFi infrastructure.
Wiacom provides configurable onboarding and access workflows for:
- employees and their personal or corporate devices;
- contractors and temporary workers;
- visitors, customers and business guests;
- remote offices and branch employees;
- partners and external service providers;
- conference and event attendees;
- managed and unmanaged BYOD devices;
- printers, displays and meeting-room equipment;
- smart building, operational and IoT devices.
Each user category can follow an appropriate registration, authentication and WiFi access journey based on organisational policies, location and device capabilities.
Enterprise Identity & Staff Connect
WiFi onboarding should work with the organisation’s existing identity infrastructure rather than introducing another independent set of user accounts.
Wiacom connects Captive Portal and Staff Connect workflows with supported enterprise identity providers, enabling employees and authorised users to authenticate through familiar organisational login experiences.
Supported Identity Providers
- Microsoft Entra ID / Microsoft 365 — OpenID Connect, including tenant authorisation and domain or group restrictions;
- Google Workspace — OAuth 2.0 / OpenID Connect;
- Okta — OpenID Connect / SAML;
- Auth0 — OpenID Connect / SAML;
- Ping Identity — OpenID Connect / SAML;
- Generic OpenID Connect — OIDC integration;
- Generic SAML — SAML 2.0 integration;
- Apple — OAuth 2.0 / OpenID Connect;
- Facebook — OAuth 2.0.
Organisations can use enterprise identity providers for employees while retaining different registration and verification methods for guests, contractors and temporary users.
Microsoft Entra ID WiFi Authentication
Organisations using Microsoft 365 can integrate Wiacom’s WiFi registration process with Microsoft Entra ID using OpenID Connect.
Supported configurations include tenant authorisation and domain or group restrictions, allowing organisations to control which users are eligible to complete registration and receive WiFi access.
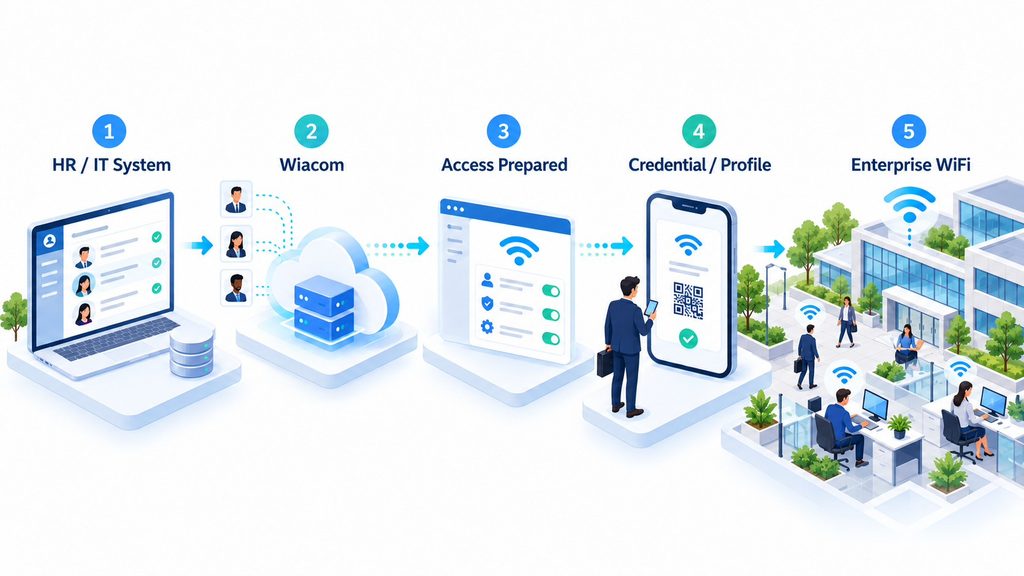
Employee → Staff Connect / Captive Portal → Microsoft Entra ID → Authorisation → WiFi Access Provisioning
Authentication establishes the user’s identity during onboarding. The subsequent WiFi access method can use WiFi Pass, Passpoint Connect or another compatible network authentication mechanism.
Self-Service Employee Onboarding
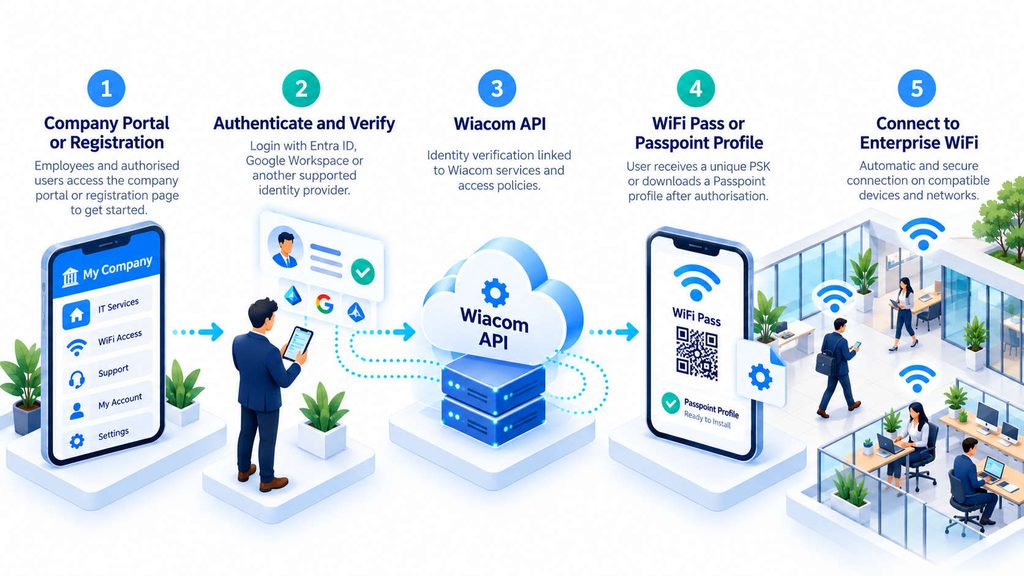
Employees and authorised users can begin registration through a Captive Portal, web link, QR code, Staff Connect page or integrated business application.
Following successful verification and authorisation, Wiacom can provide the configured network-access method without requiring IT staff to distribute a common WiFi password.
Employee → Registration → Corporate Identity Verification → Access Policy → WiFi Pass / Passpoint Connect → Enterprise WiFi
Identity-Based WiFi Provisioning
Wiacom connects verified user registration with the provisioning of individual WiFi access credentials or profiles.
Through WiFi Pass, authorised users can obtain a unique pre-shared key after Captive Portal registration on compatible networks.
Through Passpoint Connect, verified users can receive the provisioning information required to download and install a Passpoint / Hotspot 2.0 profile on supported devices.
User Verified → Access Method Selected → Unique PSK or Passpoint Profile → WiFi Connection
Access provisioning can be configured according to location, user category, device compatibility and the capabilities of the underlying WiFi infrastructure.
Identity and Policy-Based Access
Information available from an identity provider, registration process or authorised business system can help determine the appropriate onboarding and access policy.
Depending on the integration, policies can use attributes such as:
- identity provider or tenant;
- approved email domain;
- user group or department;
- employee or contractor status;
- office, site or branch;
- user role and access eligibility;
- registration or verification status;
- access duration and expiry;
- device category;
- other authorised identity or business-system attributes.
This allows businesses to combine enterprise SSO, self-service registration, individual credentials and location-specific WiFi access without requiring one onboarding method for every user.
Enterprise Applications, Employee Portals and WiFi APIs
WiFi onboarding can become part of the organisation’s existing digital workplace and employee experience.
Through supported APIs and custom integrations, business applications or employee portals can interact with Wiacom to initiate registration and prepare the appropriate WiFi access method.
For example:
Employee Portal → Authenticated User → Wiacom Integration → WiFi Pass / Passpoint Connect → Office WiFi
The same approach can be extended to approved contractor portals, enterprise applications and other identity-aware business workflows.
Guest Connect and Captive Portal
Visitors and contractors do not necessarily need the same authentication process as permanent employees.
Wiacom provides configurable Guest Connect and Captive Portal workflows for business visitors, customers, contractors, partners and event attendees.
Guest onboarding options include:
- email registration and verification;
- phone and OTP verification;
- supported social identity providers;
- QR code or web-link registration;
- terms and privacy notices;
- consent collection where required;
- time-limited access;
- pre-registration and visitor workflows;
- event and conference onboarding;
- returning-user recognition where configured.
Guest Connect can operate independently of the initial WiFi connection, enabling visitors to register before arriving or joining the network.
After successful verification, compatible deployments can also offer Passpoint profile provisioning for subsequent automatic WiFi connection.
BYOD, Device and IoT Onboarding
Not every device in a corporate environment has a browser or supports interactive user authentication.
Wiacom can support onboarding for compatible devices such as:
- employee-owned laptops and smartphones;
- printers and multifunction devices;
- meeting-room displays;
- video conferencing systems;
- smart TVs and digital signage;
- operational terminals;
- building-management equipment;
- warehouse and logistics devices;
- other supported IoT and browserless equipment.
Depending on infrastructure capabilities, devices can be associated with an owner, department, location or lifecycle and provisioned with an individual credential or appropriate access method.
WiFi Pass can provide individual PSK credentials for compatible devices, avoiding unnecessary reliance on one password shared across the entire organisation.
One Business. Multiple WiFi Access Methods.
Wiacom connects identity verification and onboarding with the appropriate WiFi access technology for employees, guests, contractors and devices across compatible existing infrastructure.
Identity-Based WiFi Access with WiFi Pass and Passpoint Connect
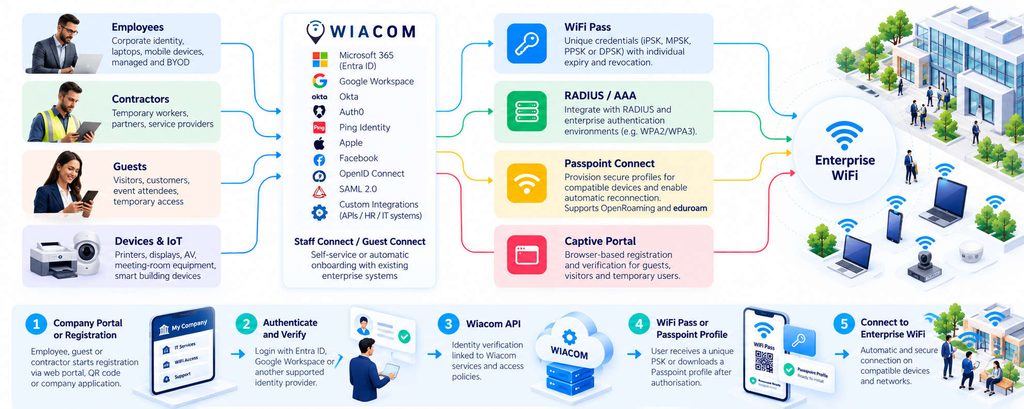
Wiacom combines user registration, identity verification and network-access provisioning within configurable enterprise WiFi workflows.
Following successful registration and authorisation through Captive Portal, Guest Connect or Staff Connect, users can be offered the access method supported by their device and network environment.
WiFi Pass — Individual Pre-Shared Keys
Wiacom WiFi Pass is available under Identity & Network Services and can be configured individually for each business location.
After completing the configured Captive Portal registration and authorisation process, eligible users can obtain a unique WiFi pre-shared key for the designated network.
Depending on the underlying infrastructure, WiFi Pass can use compatible vendor-specific technologies such as iPSK, MPSK, PPSK, DPSK or equivalent individual PSK mechanisms.
Individual credentials help organisations manage user access without distributing a single common WiFi password to everyone.
Captive Portal Registration → User Verification → Unique WiFi Pass Credential → WiFi Access
Passpoint Connect — Secure WiFi Profile Provisioning
Wiacom Passpoint Connect enables secure WiFi profile provisioning using Passpoint / Hotspot 2.0 technology on compatible devices and networks.
Following successful user verification through Captive Portal, Guest Connect or Staff Connect, Wiacom can present the information and provisioning workflow needed to download and install a Passpoint profile.
Once the profile is installed, compatible devices can authenticate and reconnect automatically when they encounter a participating WiFi network, without repeating the original registration process.
User Registration → Identity Verification → Passpoint Profile Download → Profile Installation → Automatic WiFi Reconnection
Passpoint Connect can support employees, contractors, business guests and returning visitors where the deployment and device capabilities permit.
RADIUS / AAA and Enterprise WiFi Authentication
Wiacom also supports RADIUS / AAA integration with compatible WiFi environments, including supported WPA2/WPA3 Enterprise authentication and network-access workflows.
Captive Portal identity verification, WiFi Pass credential provisioning and native WPA-Enterprise authentication are distinct mechanisms that can be combined according to the network design.
Captive Portal and Guest WiFi
Provide browser-based registration, verification, consent and network authorisation for visitors, contractors and other temporary users.
Captive Portal can also serve as the initial identity-verification stage before individual WiFi Pass credentials or Passpoint profiles are provisioned.
Work with Your Existing Enterprise WiFi
Wiacom does not require organisations to replace existing authentication infrastructure or standardise every location on the same WiFi vendor.
Businesses can add identity-based onboarding, WiFi Pass, Passpoint, Guest Connect, Staff Connect, Captive Portal, RADIUS integration and WiFi analytics according to the capabilities of each site.
One identity and onboarding layer. Multiple WiFi access technologies. Existing network infrastructure.
From Enterprise WiFi Data to Workplace Intelligence
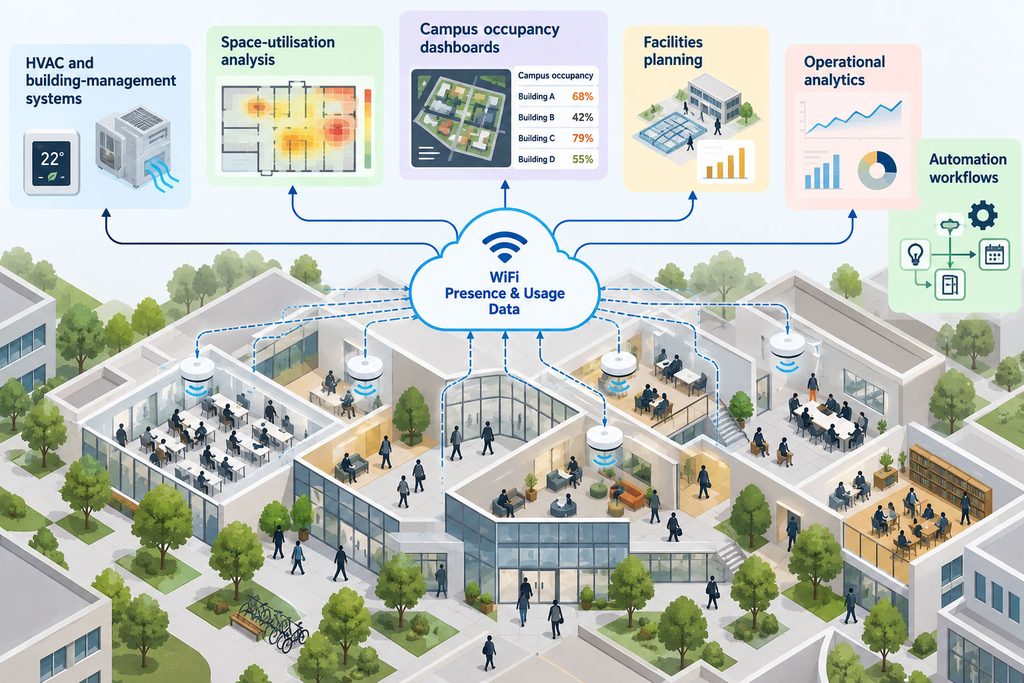
Enterprise WiFi can provide more than network connectivity. Where the required network data is available, Wiacom can help organisations use WiFi-derived presence, location and usage information within wider operational systems.
Depending on the infrastructure, aggregated presence and occupancy indicators can support:
- office occupancy analysis;
- workspace and meeting-room utilisation;
- building-management systems;
- HVAC and energy optimisation workflows;
- facilities and capacity planning;
- multi-site operational dashboards;
- visitor and venue analytics;
- business intelligence and automation.
This allows organisations to use suitable WiFi information as another input for workplace management and operational decision-making.
Data availability, accuracy, network capabilities and applicable privacy requirements determine which use cases can be implemented.
Connect Enterprise WiFi Data with Analytics, AI and Automation
Modern organisations increasingly connect identity, infrastructure, operational and workplace systems with analytics and automation platforms.
Where an organisation operates an approved analytics, AI or data platform, Wiacom can provide controlled integration points for relevant WiFi and network-access information through supported APIs and custom integrations.
Depending on the deployment, available information may include:
- WiFi registration and authentication events;
- user and device access information;
- site or building activity;
- presence and occupancy indicators;
- network usage and operational trends;
- device and connection status;
- WiFi analytics and historical reporting.
Enterprise WiFi → Identity & Network Data → Business Systems → Analytics, Automation & AI
Integrations can be designed around the organisation’s information-security policies, privacy requirements and data-governance controls.
Wiacom provides the network identity, access and integration layer; it does not require an organisation to replace its existing analytics or AI platform.
Enterprise WiFi Across Mixed-Vendor Infrastructure
Distributed businesses frequently operate different WiFi platforms across offices, branches, buildings, acquired locations and infrastructure generations.
Wiacom is vendor-agnostic and provides a common identity, onboarding, access and integration layer across compatible WiFi infrastructure.
This helps organisations standardise employee, contractor, guest and device onboarding without requiring every site to use the same network vendor.
Supported environments can include:
- Cisco Meraki;
- Cisco WLC;
- HPE Aruba;
- Ruckus;
- UniFi;
- Cambium;
- Fortinet;
- MikroTik;
- TP-Link Omada;
- other compatible WiFi infrastructure.
Specific capabilities such as Captive Portal, RADIUS, individual PSK and Passpoint depend on the network vendor, device models, firmware and available integration methods.
Wiacom can support multi-location deployments and MSP-managed environments where networks from different vendors must coexist.
Integrate Enterprise WiFi with Identity, NMS and Business Systems
WiFi authentication and onboarding do not need to remain isolated within a wireless controller.
Through APIs, webhooks and supported custom integrations, Wiacom can connect relevant WiFi information and workflows with compatible enterprise systems, including:
- Microsoft Entra ID and supported identity providers;
- enterprise SSO and authentication platforms;
- Network Management Systems (NMS);
- employee and contractor applications;
- service-management and IT operations systems;
- CRM and customer engagement platforms;
- analytics and business intelligence systems;
- building-management and workplace platforms;
- enterprise APIs and custom applications;
- approved AI and automation platforms.
The objective is to make identity, access and operational WiFi information usable beyond the WLAN management console where technically appropriate.
Access Visibility and Governance
Where supported, registration records, authentication events and individual credentials can improve traceability compared with anonymous shared-password access.
These capabilities can contribute to wider network-access governance and NIS2-related security programmes, depending on the organisation’s regulatory obligations and implementation.
Cisco Meraki Integration & Cisco Ecosystem
Cisco Developer Worldwide partner • Direct Cisco Meraki API integration • Two applications listed on the Cisco Networking App Marketplace
Wiacom integrates directly with compatible Cisco Meraki networks through the Meraki Dashboard API, allowing WiFi onboarding, guest identity and network-access workflows to interact with existing Meraki infrastructure.
Wiacom is also a Cisco Developer Worldwide partner with two applications listed on the Cisco Networking App Marketplace:
- Wiacom Guest WiFi — Captive Portal, guest identity, consent, customer engagement and WiFi analytics.
- Wiacom | Guest Connect — URL- and QR-based onboarding that can operate independently from the initial captive-portal connection journey.
For enterprises using Cisco Meraki, Wiacom can extend compatible existing environments with guest onboarding, identity integration, access workflows and business-system integrations.
Wiacom remains vendor-agnostic, allowing Meraki locations to coexist with branches using other compatible WiFi platforms.
Enterprise WiFi Implementation, MSP Integration and Technical Support
Wiacom is not limited to providing enterprise WiFi software.
We work with internal IT teams, MSPs, network integrators and multi-site organisations to implement and operate the required identity, onboarding and access workflows.
Implementation and technical services can include:
- Captive Portal implementation;
- Guest Connect and Staff Connect workflows;
- Microsoft Entra ID and enterprise identity integration;
- OIDC and SAML authentication configuration;
- WiFi Pass deployment and individual PSK provisioning;
- Passpoint Connect / Hotspot 2.0 provisioning;
- WiFi controller and SSID configuration;
- RADIUS / AAA integration;
- compatible WPA2/WPA3 Enterprise workflows;
- BYOD and IoT onboarding;
- multi-location rollout and configuration;
- API, webhook and NMS integration;
- mixed-vendor WiFi troubleshooting;
- advanced authentication and connectivity troubleshooting;
- ongoing authorised configuration changes and technical support.
For organisations managing infrastructure from multiple WiFi vendors, Wiacom provides a common operational approach while retaining the network-specific capabilities required for each environment.
Wiacom can therefore operate as the software platform, integration partner and technical operations layer around an enterprise WiFi deployment.
Enterprise WiFi Identity & Access FAQ
What is an enterprise WiFi identity and access platform?
An enterprise WiFi identity and access platform manages how employees, contractors, visitors and devices register, authenticate and obtain network access. Wiacom combines Captive Portal, identity provider integration, individual WiFi credentials, Passpoint provisioning, RADIUS and related access workflows across compatible business networks.
Can Wiacom use Microsoft Entra ID for WiFi authentication?
Yes. Wiacom supports Microsoft Entra ID integration through OpenID Connect for WiFi registration and onboarding, including Microsoft 365 organisational authentication with tenant authorisation and supported domain or group restrictions. Following verification, eligible users can receive the configured WiFi access method.
Which identity providers does Wiacom support?
Wiacom supports Microsoft Entra ID, Google Workspace, Okta, Auth0, Ping Identity, Apple, Facebook, generic OpenID Connect providers and generic SAML 2.0 integrations. The available protocol depends on the provider and configured authentication workflow.
Can employees receive a unique WiFi password after registration?
Yes. Wiacom WiFi Pass can be configured per location to provide an individual pre-shared key after successful Captive Portal registration and authorisation. The underlying WiFi infrastructure must support a compatible individual PSK mechanism such as iPSK, MPSK, PPSK or DPSK.
Can WiFi Pass credentials be managed independently?
On supported infrastructure, individual credentials can be managed, expired or revoked without changing the common WiFi password for all users. Available credential-management capabilities depend on the network integration.
Can Wiacom provide Passpoint profiles after Captive Portal registration?
Yes. Following successful verification through Captive Portal, Guest Connect or Staff Connect, Wiacom Passpoint Connect can present the provisioning information needed for users to download and install a Passpoint / Hotspot 2.0 profile. Compatible devices can then authenticate and reconnect automatically on participating networks.
What is the difference between WiFi Pass and Passpoint Connect?
WiFi Pass provides an individual pre-shared key on compatible networks. Passpoint Connect provides secure WiFi profile provisioning using Hotspot 2.0 technology. Both can follow Wiacom’s identity-verification and onboarding workflows, but use different network-access mechanisms.
Does Wiacom support employee and contractor BYOD?
Yes. Wiacom supports self-service registration and identity-based onboarding for compatible employee and contractor devices, with access methods determined by the business policy, device capabilities and underlying WiFi network.
Can Wiacom onboard printers and IoT devices?
Yes. Wiacom can support controlled onboarding for compatible printers, displays, operational devices and browserless IoT equipment. Available authentication methods depend on device capabilities and WiFi infrastructure.
Can Wiacom work with RADIUS and WPA2/WPA3 Enterprise?
Yes. Wiacom can integrate with compatible RADIUS / AAA and WPA2/WPA3 Enterprise environments. Native enterprise authentication and identity-provider-based Captive Portal registration are different workflows and can be combined where supported.
Can Wiacom support multiple offices and branches?
Yes. Wiacom supports multi-location environments with configurable onboarding and access services by location. Organisations can manage employees, guests and network-access workflows across compatible distributed WiFi infrastructure.
Does Wiacom require replacing existing WiFi hardware?
Not necessarily. Wiacom operates above compatible existing WiFi infrastructure. Available Captive Portal, WiFi Pass, Passpoint and RADIUS capabilities depend on the vendor, controller, firmware and supported integration methods.
Can Wiacom work across different WiFi vendors?
Yes. Wiacom is vendor-agnostic and supports compatible mixed-vendor environments involving Cisco Meraki, Cisco WLC, HPE Aruba, Ruckus, UniFi, Cambium, Fortinet, MikroTik, TP-Link Omada and other infrastructure.
Can WiFi data be integrated with building-management systems?
Potentially. Where suitable WiFi presence, occupancy or operational data is available, Wiacom can make relevant information available to compatible building-management, analytics and workplace systems through supported integrations, subject to privacy and data-governance requirements.
Can Wiacom integrate with enterprise AI and automation platforms?
Yes, where appropriate APIs or custom integration methods are available. Relevant WiFi identity, authentication, access and operational data can be made available to approved enterprise analytics, automation or AI systems according to the organisation’s security and privacy requirements.
Can Wiacom support MSPs managing mixed WiFi environments?
Yes. Wiacom can work with managed service providers and network integrators to implement identity-based onboarding, multi-location WiFi access, vendor-specific integrations, network troubleshooting and technical operations across compatible infrastructure.
Build Enterprise WiFi Around Identity, Individual Access and Existing Infrastructure
Enterprise WiFi is no longer only about providing an SSID and network connectivity.
Employees need convenient, identity-based onboarding. Contractors require controlled access. Visitors need straightforward Guest WiFi. BYOD and IoT devices may require individual credentials. IT teams need operational visibility across locations and WiFi vendors.
Wiacom brings these requirements together through a common identity, onboarding, network-access, analytics and integration layer while allowing organisations to retain compatible existing WiFi infrastructure.
Connect Microsoft Entra ID, Google Workspace, Okta and other supported identity providers with registration workflows. Issue individual WiFi Pass credentials or provision Passpoint profiles after verification. Extend the same approach across compatible offices, branches and managed networks.
Enterprise Identity. WiFi Pass. Passpoint Connect. Guest WiFi. Connected Devices. One Adaptable Access Platform.
WiFi Identity, Access, Engagement and Analytics for Marketing, IT & Operations Teams
US, UK, EU: +40 721 260 892
info@wiacom.ai
© 2026 Wiacom
All rights reserved


